Portfolio proof of concept
AI and MCP access governance
May to July 2026.
A working demonstration of structured review for AI agent integrations and MCP-connected tools. Each integration is treated as a governed access request, not unmanaged developer tooling.
AI agents and MCP-connected tools can receive data, call APIs and trigger actions across SaaS, cloud and internal platforms. The platform puts a repeatable control loop in front of that, using fictional vendors and mock intake data.
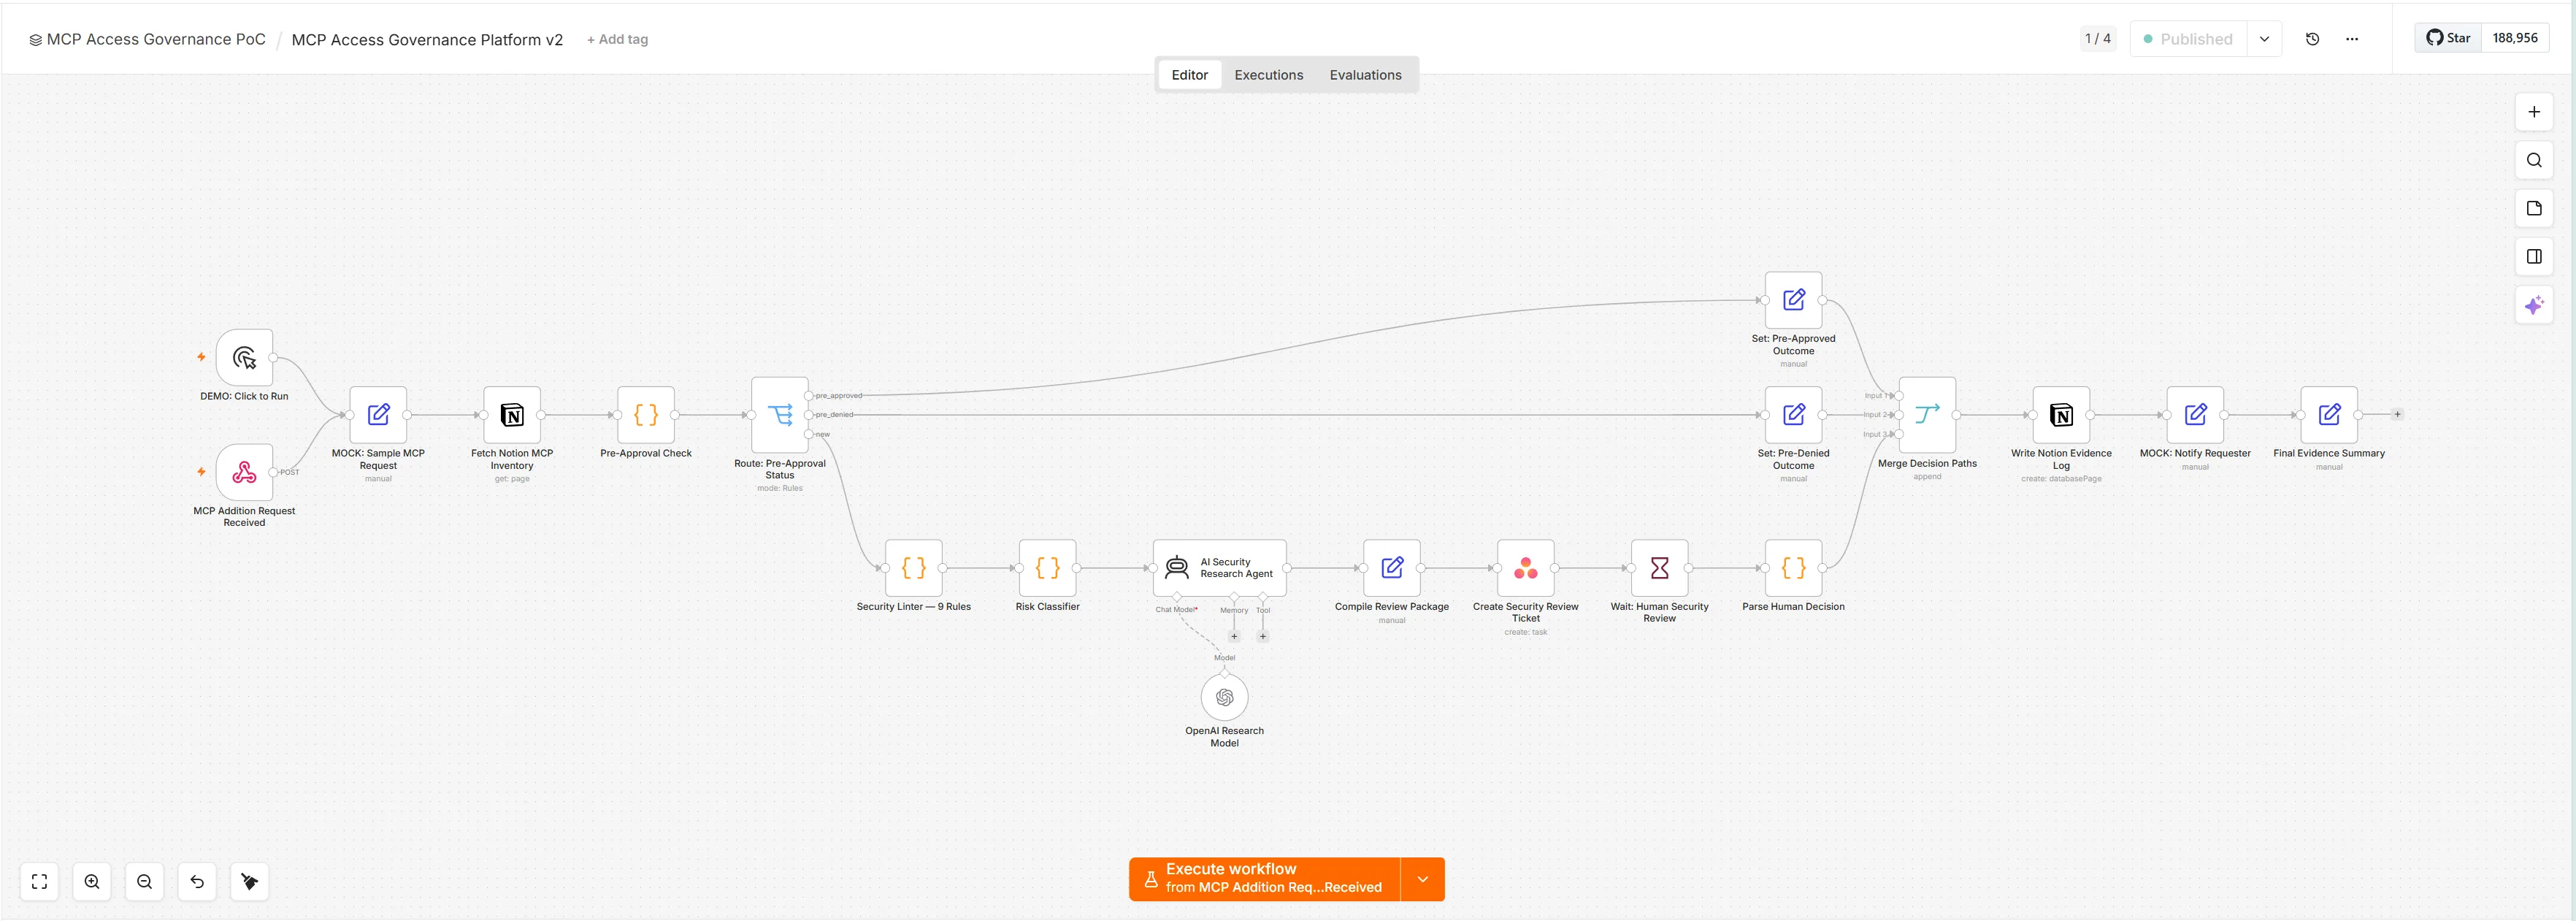
The control loop
- Request. Capture the owner, purpose, data class, environment and tool details.
- Classify. Evaluate privilege, data exposure, tool behaviour and vendor maturity.
- Review. Route material risk to an accountable reviewer, with conditions where needed.
- Evidence. Record the final decision in a durable, structured format.
What's in it
- One runnable n8n workflow
- Eight control objectives and four risk levels
- 42 passing tests
Portfolio proof of concept. Not a production deployment, certification or attestation. My approach to MCP governance has moved on since.
More projects
- Ask the Atlas: an interactive questionnaire over the knowledge base Interactive capstone, October 2026
- The Offerings Atlas: mapping what 166 AI platforms cover, and what they don't Knowledge base case study, October 2026
- A local gateway for headless Claude and Codex Personal tooling, October 2026
- Building a governed AI agent on an open knowledge base Agent build case study, September 2026
- Runner: Claude study game Study game, July to September 2026
- Securing Claude Cowork: controls, gaps and safer defaults Practitioner reference, Version 1.4
- Human, script or AI? Spotting AI-driven attacks in the SOC SOC advisory white paper, Version 5
- RESYNTH research pipeline Open-source tool, First released June 2026
- AWS security architecture case study Fictional case study, April 2026
- Incident response planning portfolio Planning portfolio, April 2026